Getting ISO 27001 certified is one thing. Making it work in practice is another.
When I took on the responsibility of leading Irisgruppen through the ISO 27001 certification process, I quickly realized that one of the biggest challenges wasn't necessarily understanding what the standard required.
It was figuring out how to translate those requirements into something practical, relevant, and sustainable for our organization.
ISO 27001 provides a framework, but it doesn't hand you a ready-made solution.
Throughout the process, I spent considerable time breaking down requirements, interpreting their purpose, and finding ways to make them concrete and applicable to our operations.
I kept coming back to three questions:
🔹 What does this requirement actually mean in practice?
🔹 How can we make it relevant and proportionate to our organization?
🔹 How do we ensure it continues to work long after certification?
That approach helped us successfully achieve ISO 27001 certification. But more importantly, it shaped how I developed the supporting processes, documentation, and tools.
Because certification isn't the finish line.
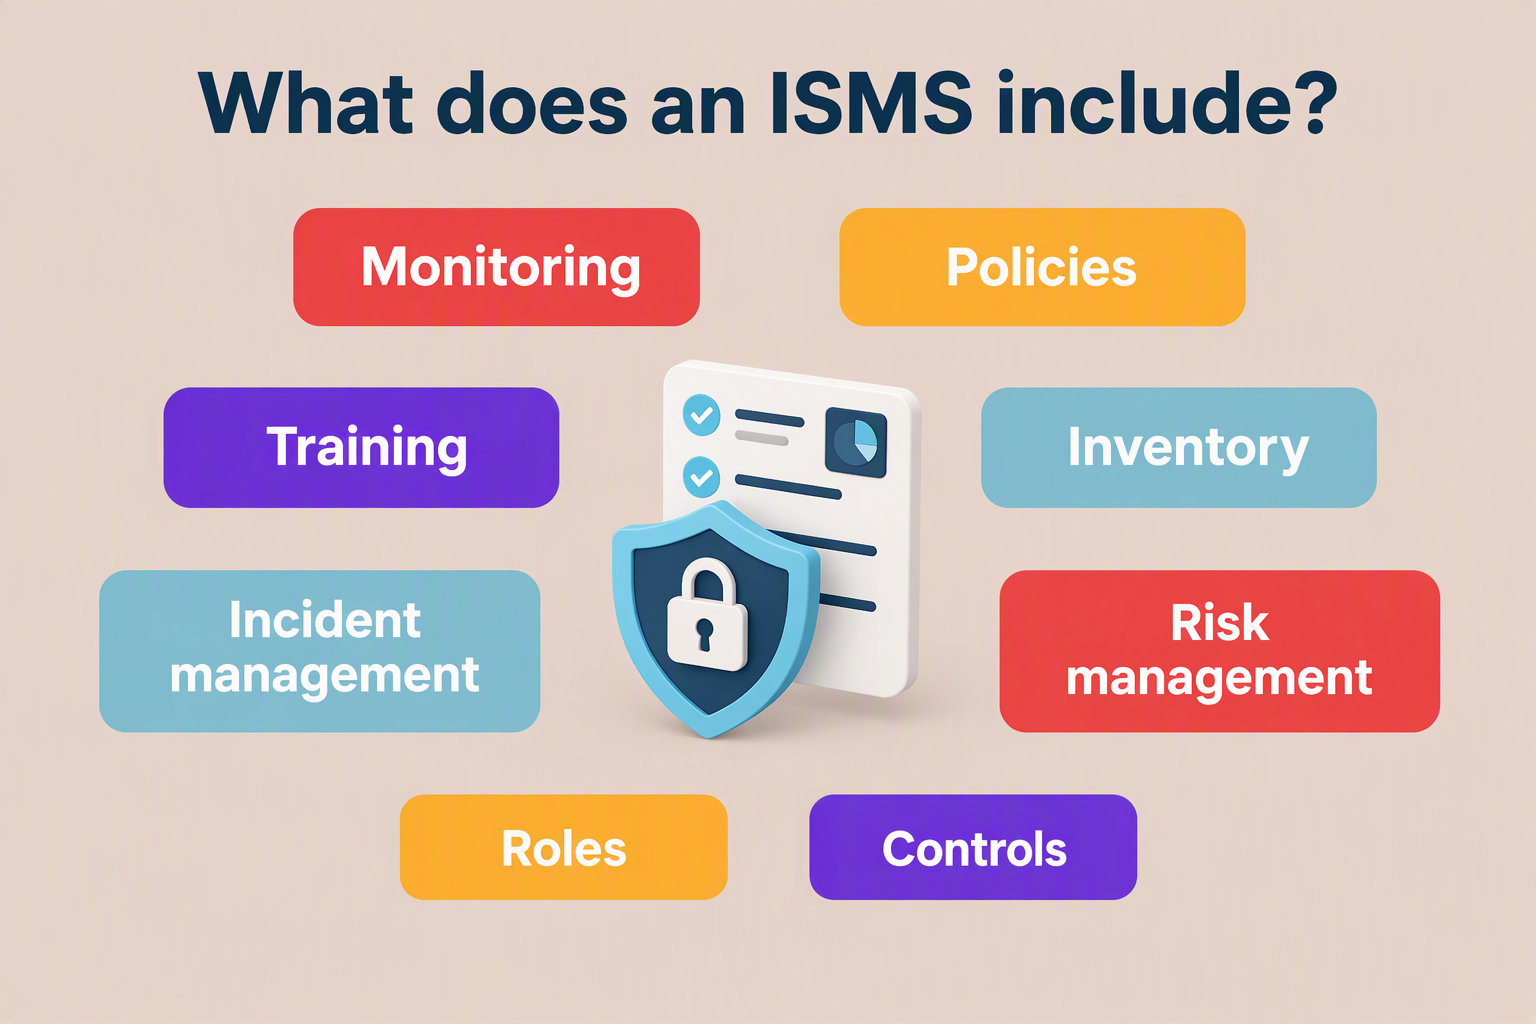
An effective Information Security Management System (ISMS) requires continuous risk management, internal audits, follow-ups, improvements, and adaptation as the organization evolves.
And that's exactly what I wanted the framework to support.
Drawing on this experience, I've developed a comprehensive ISO 27001 toolkit designed to help organizations translate requirements into practical actions.
The focus is on making the framework:
✅ Understandable — Breaking down complex requirements into clear, actionable steps.
✅ Scalable — Adaptable to different organizational sizes, structures, and needs.
✅ Practical — Supporting actual ways of working, not just documentation.
✅ Sustainable — Designed for continuous improvement and long-term use.
📄 I'm sharing a small preview of the material as a downloadable PDF, offering a glimpse into how I've approached making ISO 27001 more accessible and actionable.
My biggest takeaway from this journey?
A successful ISMS isn't the one that looks best on paper. It's the one that actually works in practice.